NIS2 in Production: How to Secure Compliance Quickly
Disaster Recovery & Backup as the Foundation for Resilient OT Systems
The NIS2 Directive (Network and Information Security Directive 2) of the European Union has been in force in Germany since December 6, 2025 (NIS2UmsuCG). It obliges affected companies to implement demonstrable cybersecurity measures not only in IT, but explicitly in production and the OT environment as well.
Whether a company falls within the scope of NIS2 can be checked for Germany using the BSI NIS2 applicability check. For companies in other EU member states, a corresponding check must be carried out via the relevant national authority.
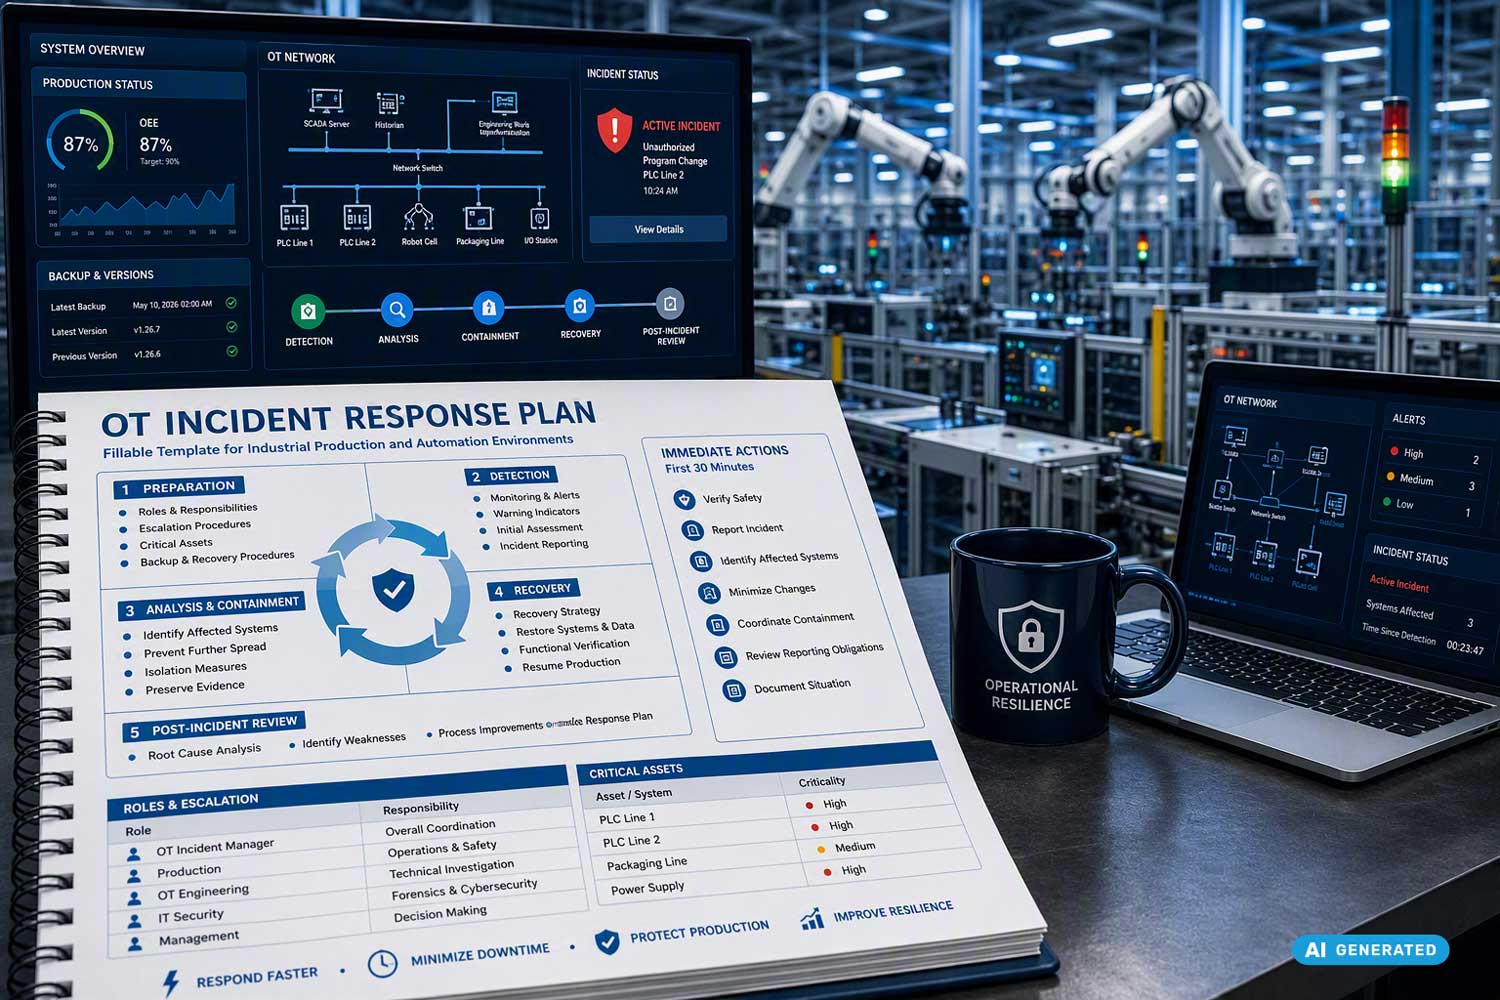
The focus is not only on protection against cyberattacks, but above all on the ability to restart production systems quickly and in a controlled manner after a security incident.
What Is NIS2 and Who Does It Affect?
The NIS2 Directive applies to companies with 50 or more employees or an annual turnover of EUR 10 million, provided they operate in critical or important sectors – including many manufacturing and industrial companies.
Key new requirements include:
- demonstrable technical and organizational measures
- resilience and recovery capability instead of prevention alone
- clear accountability all the way up to executive management
For manufacturing companies, this means specifically: not just avoiding attacks, but being able to resume operations quickly after incidents.
Why NIS2 Particularly Affects the Shopfloor
While established security and backup processes exist in IT, OT has grown historically in many companies. The following are often missing:
- complete transparency across OT systems
- up-to-date documentation of configuration states
- tested emergency and recovery plans
This results in key NIS2 requirements in the OT environment:
- transparency across systems and configurations
- controlled and traceable access
- audit-proof documentation
- reproducible system and configuration states
- verifiable audit evidence
Disaster recovery and backup management are therefore an essential part of business continuity.

Audit Trails & Evidence Documentation
All security-relevant actions are logged completely and immutably – audits become plannable.
GxP-Workflow
Optional four-eyes principle for regulated industries such as pharmaceutical, medical technology, and food production.
Pragmatic NIS2 Roadmap
- Analysis of OT systems and processes
- Pilot (e.g., a single line or one plant)
- Definition of backup cycles, roles, and alerting
- Rollout to additional sites
- Generate audit reports at the push of a button
Conclusion: NIS2 Cannot Be Met Without Reliable Recovery
For production and OT environments, NIS2 specifically means:
- tested restore scenarios for critical assets
- tamper-proof backups
- recovery times that fit production – minutes instead of days
Get Expert Advice Now: NIS2-Compliant OT Backups & Disaster Recovery
In a non-binding consultation, we will analyze together:
- which OT systems are critical for your NIS2 compliance
- how resilient your current backup and restore processes are
- how business continuity and audit evidence can be secured technically
FAQ: NIS2, Backup & Disaster Recovery in Production
What is the NIS2 Directive?
The NIS2 Directive is the revised EU directive on network and information security. It obliges affected companies to implement and demonstrate technical and organizational measures to improve their cyber resilience.
Which companies are affected by NIS2?
In principle, NIS2 affects companies with 50 or more employees or an annual turnover of EUR 10 million, provided they operate in critical or important sectors. Whether a company is affected should be checked against the applicable national regulations.
Why is NIS2 particularly relevant for manufacturing companies?
Because production downtime can have significant economic consequences. NIS2 therefore requires not only protective measures against attacks, but also the ability to restore affected systems quickly and continue operations.
What role do backups play in NIS2 compliance?
Backups are a central foundation for business continuity and disaster recovery. They enable the restoration of machine, PLC, HMI, and SCADA configurations after technical failures or cyberattacks.
Is a backup alone enough to meet NIS2 requirements?
No. In addition to backups, access controls, documentation, incident response processes, risk analyses, and regularly tested recovery procedures are required, among other things.
Why are restore tests so important?
Only a successfully tested restore proves that a backup is actually usable in an emergency. Regular recovery tests are therefore an important part of a resilient OT security strategy.
How does eguide4DATA support the implementation of NIS2?
eguide4DATA supports companies with automated data backup, versioning, role-based access concepts, audit trails, evidence documentation, and optional GxP workflows for regulated industries.
How can a company get started with implementation?
A sensible starting point is analyzing the existing OT systems, defining backup and recovery processes, and piloting step by step in individual production areas.